Skip to content
Blog

Notes from inside hacked WordPress sites.

Threat research, real-world compromise walkthroughs and plain-English guides from the RedSecLabs team.

All articles

Blog/ 16 min read

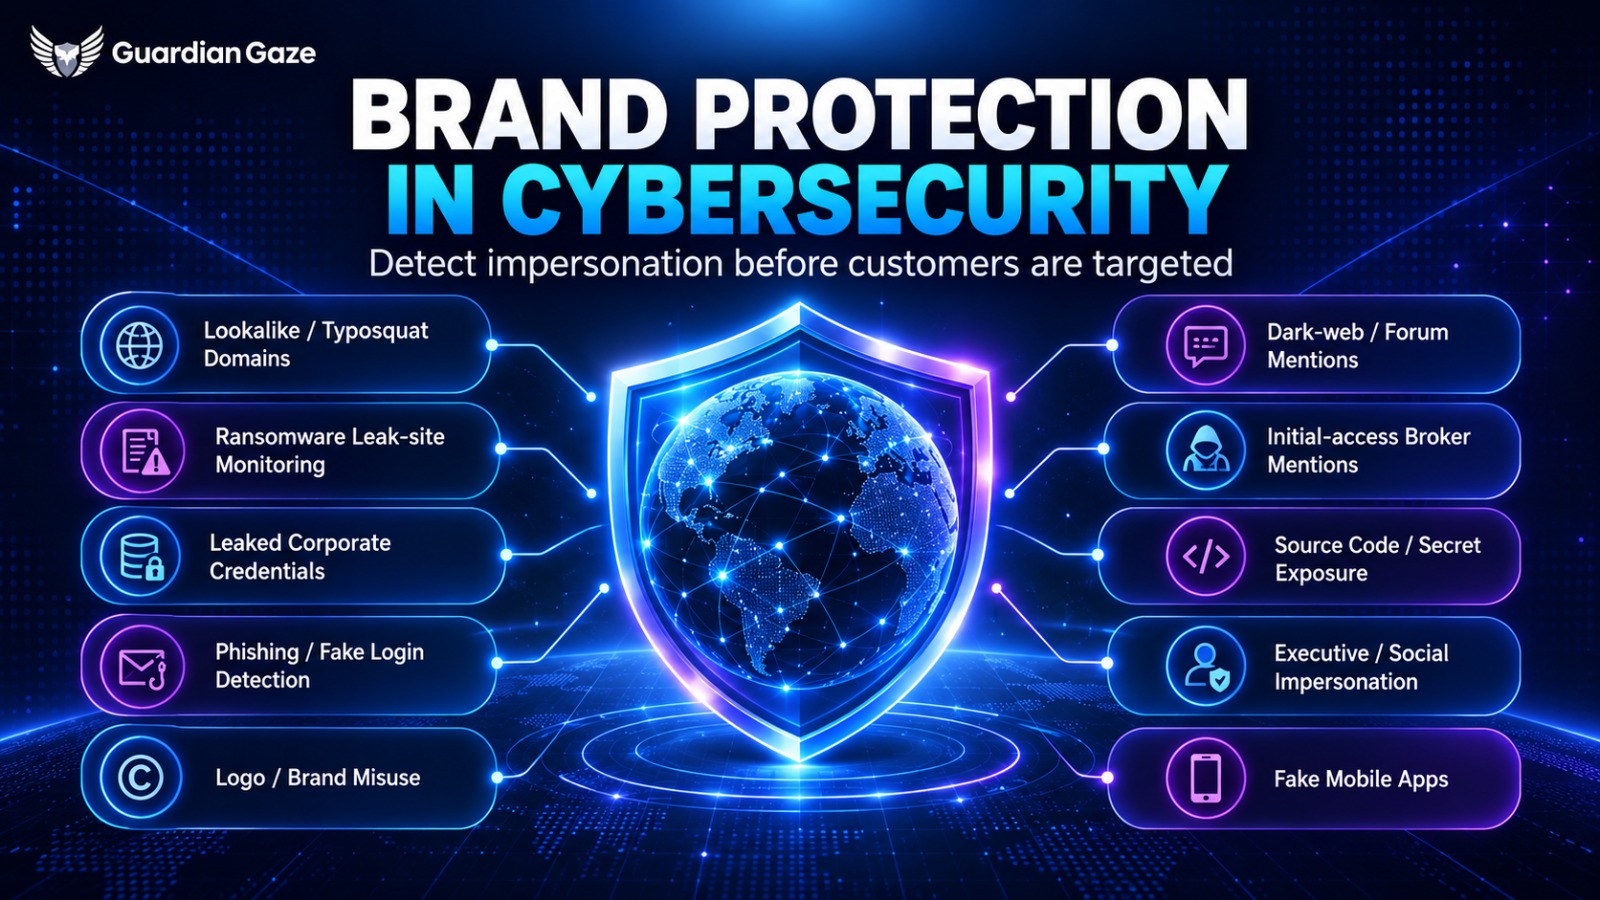
Brand Protection in Cybersecurity: How to Detect Impersonation Before It Spreads

The useful question is not whether someone can copy your logo. It is how early you can see the infrastructure,…

Farhan Memon · September 2026
Blog/ 17 min read

EASM vs Vulnerability Management: What Each Finds and Misses

Security teams rarely lose sleep over the server that is already in the vulnerability scanner. The awkward one is the…

Farhan Memon · August 2026
Blog/ 11 min read

WordPress Backdoor Detection: Plugin vs Server-Side Scanning

A backdoor is built to survive the obvious cleanup. This guide explains what local WordPress scanners, remote analysis, host-level tools…

Farhan Memon · August 2026
Blog/ 19 min read

WordPress Supply Chain Attack: Detecting Trojanised Plugins

How poisoned dependencies, compromised build pipelines and trusted plugin updates reach WordPress sites, what the 2026 incidents teach us, and…

Farhan Memon · August 2026
Blog/ 4 min read

Guardian Gaze 2.5.0: Free WordPress Security Alerts

Product Update  |  Version 2.5.0 The WordPress dashboard should not be the only place you discover that an administrator has…

Aqsa · August 2026
Blog/ 28 min read

From Managed WordPress to Wazuh: An Agentless Guardian Gaze SIEM Integration

During a Guardian Gaze SOC integration, the RedSecLabs (RSL) team needed to bring WordPress security telemetry into an existing Wazuh…

Farhan Memon · August 2026
Blog/ 15 min read

WordPress SIEM Monitoring: Detect Rogue Admins and Backdoors with Guardian Gaze and Wazuh

Series Context Article 1 covers the incident-response case: multiple unauthorised administrators, wp2shell exposure analysis, backdoor checks and recovery. This article…

Farhan Memon · August 2026
Blog/ 15 min read

Inside a wp2shell WordPress Hack: Rogue Admin Accounts, Backdoors and Incident Response

Case-study Boundary The affected pharmaceutical organisation is anonymised. The investigation confirmed multiple unauthorised WordPress administrator accounts. The circumstances were consistent…

Aqsa · August 2026
Blog/ 10 min read

AI WordPress Security Plugin: How LLM Detection Catches What Rules Miss (2026)

Every WordPress security plugin before 2024 worked the same way: maintain a database of known malware signatures, compare your files…

Farhan Memon · July 2026
Blog/ 8 min read

Wordfence Review 2026: What It Gets Right, What It Misses, and When to Use It

Wordfence is the leading free WordPress security plugin, but its in-process scanner has limitations that modern malware can exploit. Here's…

Farhan Memon · July 2026

Get new posts in your inbox.

One email per post. Threat walkthroughs, agency playbooks, and product updates. Unsubscribe anytime.

Subscribe →